Understanding WordPress Security Audits
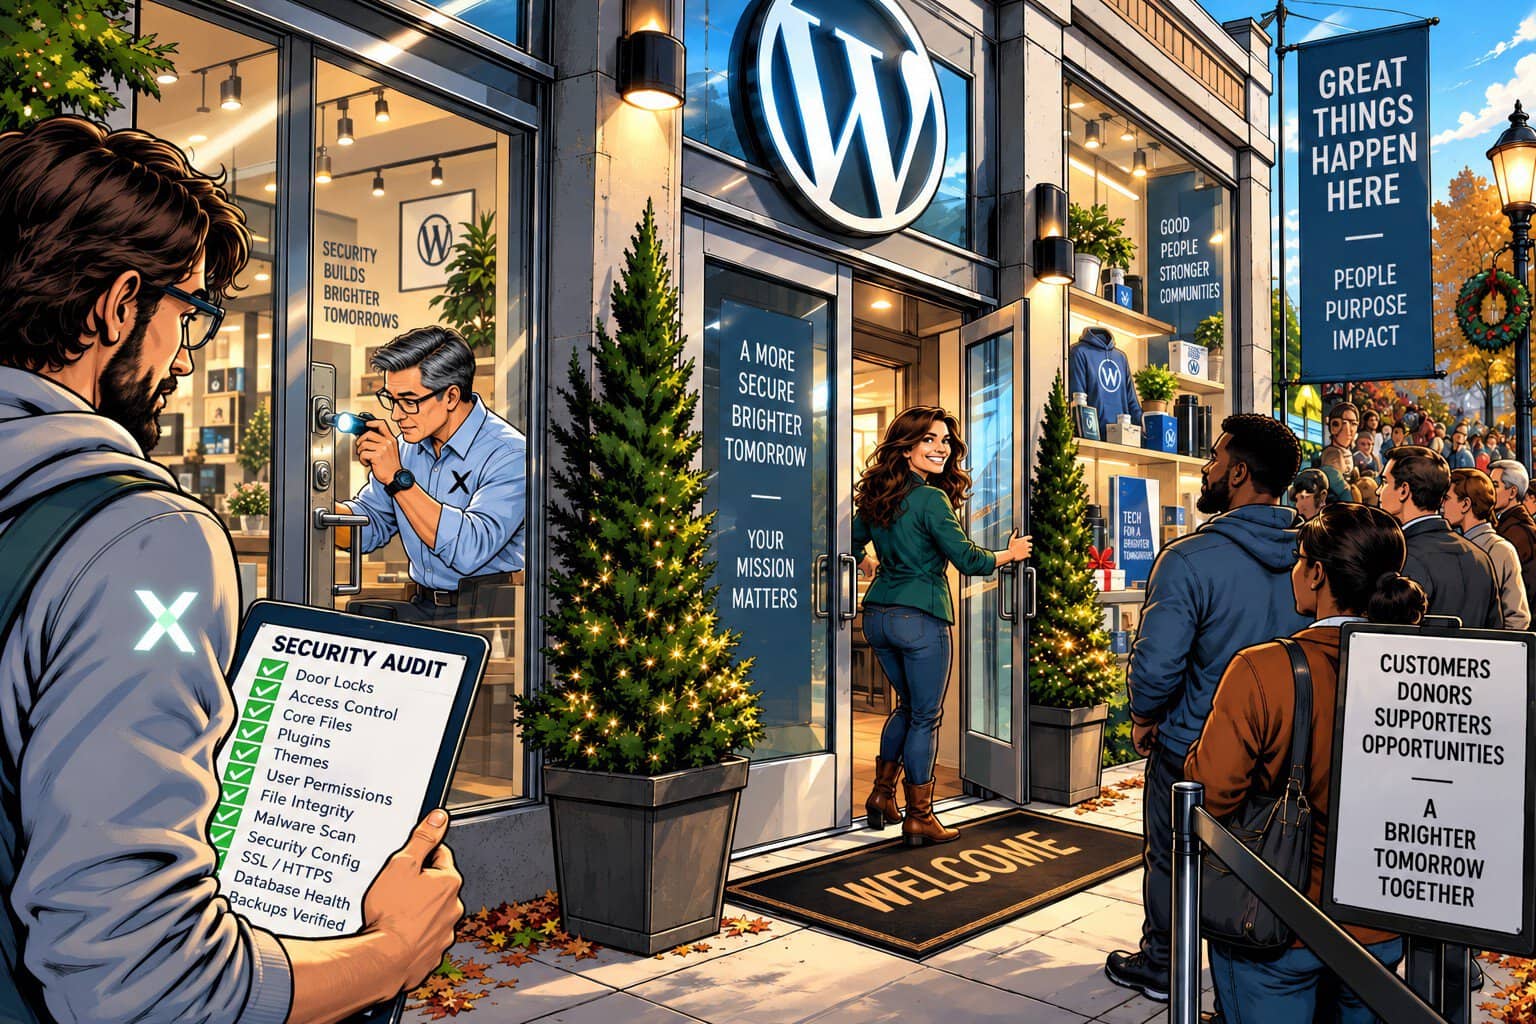
A WordPress security audit is a thorough evaluation of your website’s security posture to identify potential vulnerabilities before they lead to operational interruptions or data compromise. For businesses that cannot afford downtime or breaches, these audits serve as a proactive safety check. They expose hidden risks like outdated software, insecure configurations, or plugin weaknesses that could be exploited.
User X can help identify hidden security risks and keep your WordPress website protected with ongoing expert support.
How Security Audits Work
Security audits typically include automated vulnerability scans combined with expert manual review. Key components are:
Vulnerability Scanning: Automated tools inspect your WordPress core, plugins, and themes to detect known security loopholes. This helps prioritize patches before exploits emerge.
Permission and Access Review: Analyzing user roles, file permissions, and login protocols mitigates insider risks and unauthorized access, which could cause data leaks or content tampering.
Plugin and Theme Analysis: Plugins and themes are common breach vectors. Audits check for outdated versions, insecure code, and abandoned plugins that increase exposure.
Malware Detection: Regular scans identify malicious code injections or infections early, preventing spread and serious operational damage.
Each of these checks helps uncover problems that could otherwise lead to downtime, lost revenue, or damaged customer trust.
Common Security Issues Identified by Audits
Security audits frequently uncover:
- Outdated WordPress core or plugins leaving known vulnerabilities open.
- Weak or reused passwords risking unauthorized login.
- Excessive user privileges allowing unintended changes.
- Misconfigured security settings like directory listing or improper SSL setup.
- Presence of insecure or abandoned plugins increasing vulnerability footprint.
Addressing these issues ahead of time prevents incidents that could result in costly emergency fixes or prolonged downtime.
The Business Impact of Neglected Security Audits
Ignoring regular security audits exposes your organization to serious consequences:
- Data Breaches: Sensitive customer or organizational data could be stolen, leading to regulatory penalties and loss of trust.
- Website Downtime: Cyberattacks or injected malware might crash your website, interrupting sales and service availability.
- Reputation Damage: Security incidents can quickly erode customer confidence and damage brand perception.
- Financial Costs: Beyond immediate repair expenses, lost revenue and liability risks significantly impact your bottom line.
A proactive audit strategy helps avoid these preventable business disruptions.
Implementing a Practical WordPress Security Audit Routine
Establish a recurring audit schedule appropriate to your website’s update frequency and exposure. Steps include:
- Plan quarterly or biannual audits aligned with major WordPress updates.
- Combine automated scanning tools with expert manual assessment for thorough coverage.
- Verify and remediate findings promptly to maintain continuous protection.
- Integrate audits within your ongoing WordPress maintenance strategy for operational continuity.
Regular audits serve as a critical checkpoint, revealing risks before they develop into business problems.
Keep Your WordPress Site Secure With User X
To safeguard your WordPress site and ensure reliable performance, consider partnering with User X Hero Support. Our expert team specializes in tailored audit strategies, maintenance, and security solutions that keep mission-critical websites operating smoothly with minimal risk.